
A DPS Primer
CLI baseline: The examples use Azure IoT CLI preview extension
azure-iot1.0.0b2, released 6 October 2026. Last reviewed against current Microsoft Learn guidance 5 November 2026. Release notes.
Welcome back to this series of posts exploring the latest features of Azure IoT Hub, Device Provisioning Service (DPS), and Azure Device Registry (ADR).
The previous post introduced the new features and gave an overview of what we can expect in this post series.
In this post, we’ll dive deeper in the Azure Device Provisioning Service and how we can use the new features.
How it works
For this X.509 onboarding flow, the device authenticates to the Device Provisioning Service (DPS) using a bootstrap certificate and submits a certificate signing request (CSR) during provisioning; its private key stays on the device. DPS validates the onboarding credential and, when Azure Device Registry (ADR) certificate management is enabled, requests a separate operational certificate from the certificate authority (CA) selected by the ADR certificate policy linked to the DPS enrollment. DPS returns the issued certificate chain and Hub assignment; the device then uses the operational certificate to authenticate to the Azure Internet of Things (IoT) Hub. The device does not connect to ADR directly. DPS is required for the IoT Hub preview; ADR certificate management is optional. See the Introduction for the series-wide changes.
What’s new in this version?
The device code now uses Microsoft.Azure.Iot.Device 2.0.0-preview4:
one unified ConnectionClient for DPS and the Hub, and TelemetryClient for
our messages. I’ve removed the custom C# provisioning protocol, not the
configuration and durable CSR/key/chain handling. Standard symmetric-key/X.509
and both CSR flows remain on the existing Hub, with its endpoint/profile discovered
through DPS. This is still a preview.
Note: This guide uses PowerShell for all commands and scripts. While Azure CLI commands work identically in bash/zsh, PowerShell is recommended for Windows environments and provides consistent cross-platform support. If you’re using Linux/macOS, you can install PowerShell Core or adapt the commands to bash syntax.
Contents
- Introduction
- A DPS Primer (this post)
- Creating DPS, IoT Hub and ADR Instances
- Understanding X.509 and CSR Workflows
- The Device Application
What is Device Provisioning Service?
Let’s start with the basics. Before we write code or create Azure resources, you need to understand what DPS does and why it matters for your IoT deployment.
Azure IoT Hub Device Provisioning Service (DPS) is a helper service for IoT Hub that enables zero-touch, just-in-time provisioning to the right IoT hub without requiring human intervention.
Why Use DPS?
You might be wondering: "Can’t I just register devices manually in IoT Hub?" You can, but let’s see why that doesn’t scale:
Traditional Approach (Manual Registration)
- Register each device manually in IoT Hub
- Hardcode connection strings in device firmware
- Difficult to reassign devices to different hubs
- Doesn’t scale beyond a few devices
- Manual certificate management and rotation
DPS Approach (Zero-Touch Provisioning)
- Devices automatically register themselves
- No connection strings hardcoded
- Devices can be reassigned dynamically
- Scales to millions of devices
- Automated certificate issuance and lifecycle management
Key Benefits
Now that you understand the difference, here are the concrete advantages of using DPS:
- Scale: Provision thousands or millions of devices without manual intervention. Devices can self-register when they first come online.
- Security: No connection strings hardcoded in device firmware. Devices use cryptographic attestation (symmetric keys, TPM, or X.509 certificates) to prove identity.
- Flexibility: Devices can be reassigned to different IoT Hubs based on business logic, geolocation, or load balancing.
- Multi-tenancy: Different devices can automatically be directed to different IoT Hubs based on enrollment configuration.
- Separation: Separation between bootstrap and operational credentials for devices.
Optional ADR Certificate Management (Preview)
When certificate management is enabled, DPS can coordinate ADR issuance of operational X.509 certificates during provisioning using a Certificate Signing Request (CSR). This optional capability doesn’t replace the device’s onboarding credential. You can use a Microsoft-managed root CA or bring your own CA; DPS remains required for every IoT Hub preview scenario, whether certificate management is enabled or not. See the certificate management overview.
What’s New: Microsoft Certificate Management
The unified SDK now handles this repository’s CSR provisioning flow. The earlier custom transport has been removed. The current service workflow is that DPS validates the device’s onboarding credential and coordinates issuance of an operational certificate from the ADR namespace’s issuing CA:
Traditional X.509 Workflow
graph TD
    CA["Your CA (PKI)"] -->|creates| Chain["Root and intermediate certificates"]
    CA -->|issues ahead of time| DeviceCert["Per-device X.509 certificate"]
    Chain -->|trusted by| DPS["DPS enrollment"]
    DeviceCert -->|installed on| Device["Device"]
    Device -->|onboards with X.509| DPS
    DPS -->|assigns| Hub["IoT Hub"]
    Device -->|connects with X.509| Hub
🆕 New CSR-Based Workflow
flowchart TB
    subgraph enrollment["Enrollment setup"]
        direction LR
        DPSProfile["DPS enrollment"] -->|references policy| Policy["ADR certificate policy"]
    end

    subgraph request["Device onboarding"]
        direction LR
        DeviceRequest["Device: generate keypair and CSR"] -->|CSR and onboarding attestation| DPSValidate["DPS: validate credential"]
    end

    subgraph issuance["Operational certificate issuance"]
        direction LR
        ADR["ADR: select policy's issuing ICA"] -->|use policy| CA["Microsoft-managed CA: issue chain"]
        CA -->|issued chain| ADRReturn["ADR: return chain to DPS"]
    end

    subgraph return["Return to device"]
        direction LR
        DPSReturn["DPS: return chain and Hub assignment"] --> DeviceInstall["Device: install chain"]
    end

    Hub["IoT Hub"]
    DPSProfile --> DPSValidate
    Policy --> ADR
    DPSValidate -->|request issuance| ADR
    ADRReturn -->|return chain| DPSReturn
    DeviceInstall -->|connect with operational X.509| Hub
    ADR -->|synchronize CA certificates| Hub
The device generates the CSR and keeps its private key; it never leaves the device. Its onboarding credential authenticates to DPS, while the enrollment references the separate ADR certificate policy for operational issuance. The policy belongs to an ADR intermediate CA and controls device-certificate validity. Current IoT Hub workflows support operational-certificate renewal without reprovisioning; follow the current service documentation for the device flow.
Key advantages:
- No need to manage your own CA infrastructure
- Private keys never leave the device
- Certificates issued just-in-time
- Automated lifecycle management
- Reduced operational complexity
Azure Device Registry (ADR) Integration
Azure Device Registry (ADR) is Microsoft’s centralized device registry and management plane. It represents IoT Hub devices as Azure Resource Manager resources, enabling governance through RBAC, tags, resource groups, and cross-hub queries with Azure Resource Graph.
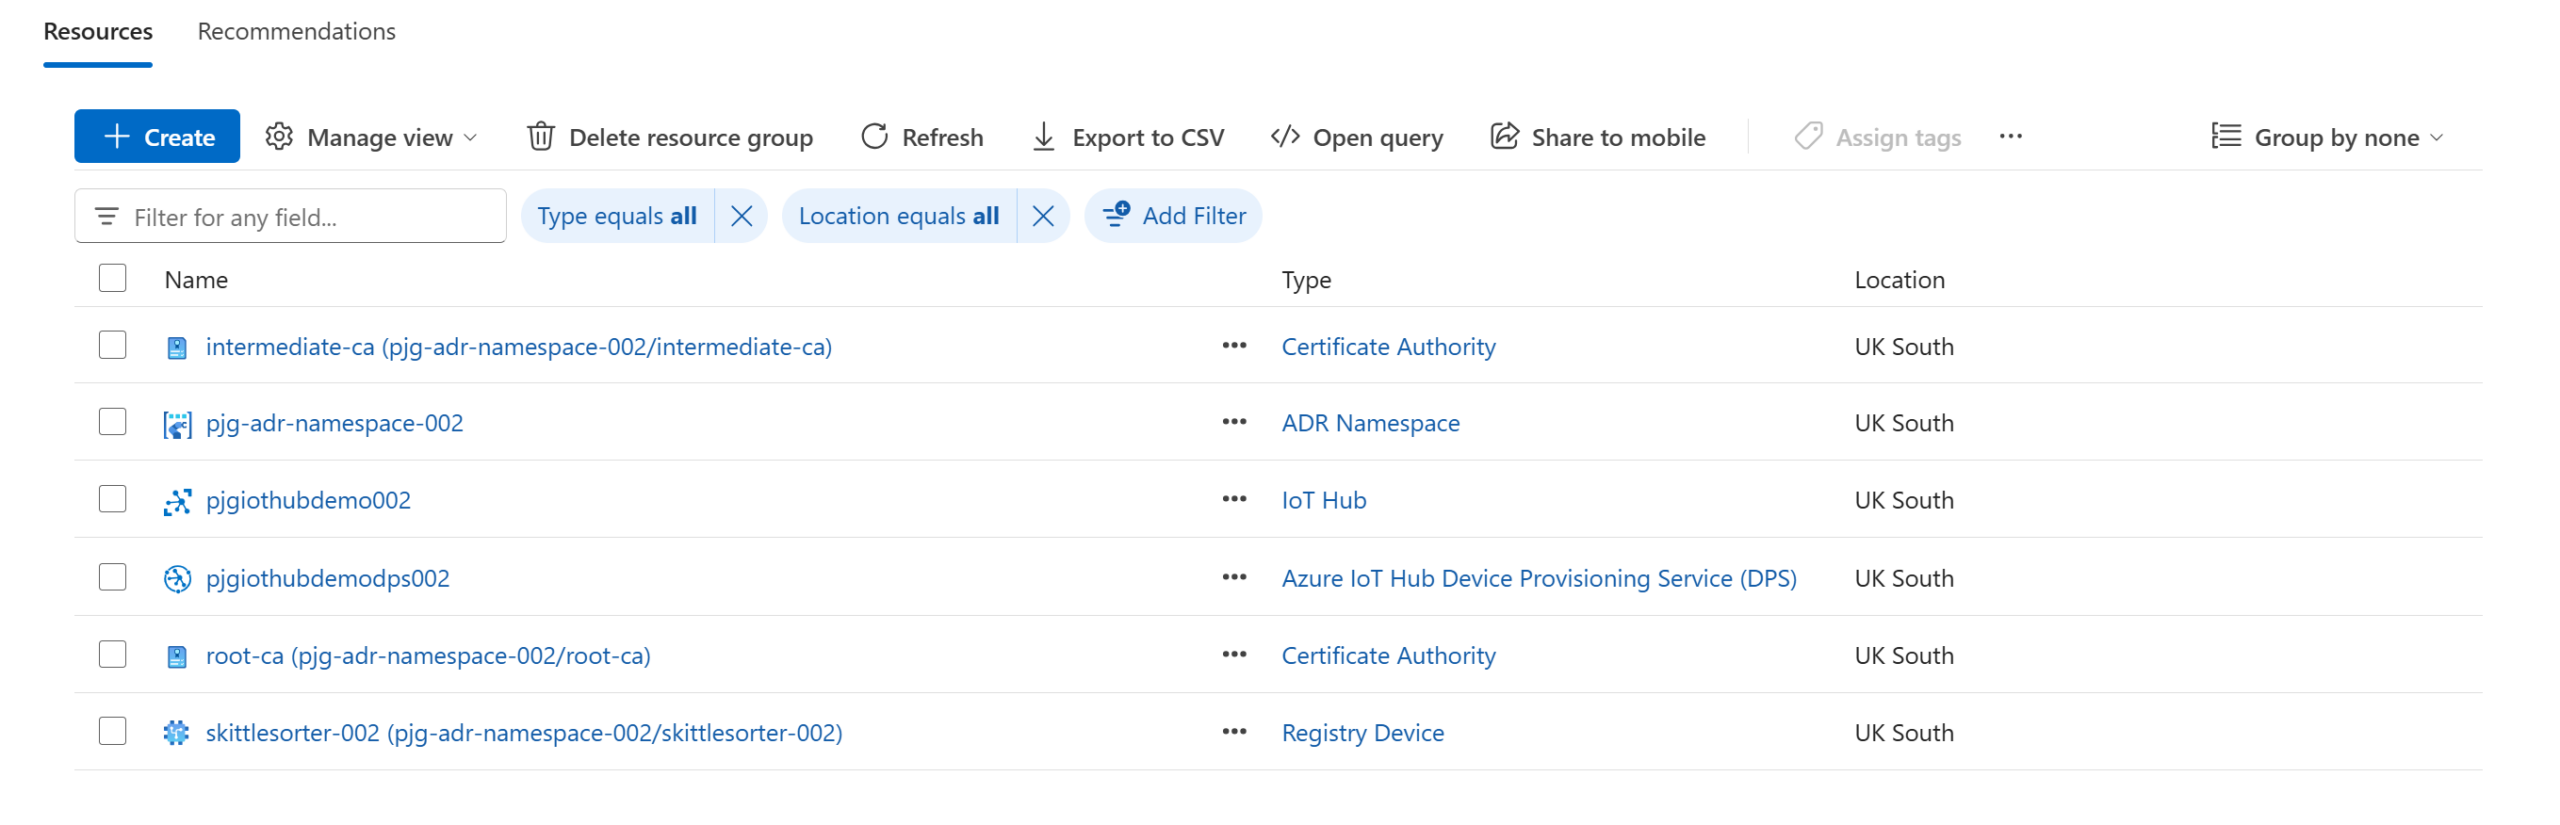
ADR is generally available for Azure IoT Operations. Its integration with Azure IoT Hub is a separate public preview. Each IoT Hub links to one ADR namespace, while multiple hubs can share a namespace. You can create a new Hub or connect an eligible existing Hub. Connecting an existing Hub to a namespace is permanent and can’t be reversed. This series’ setup script creates a dedicated new Hub; see the current getting-started guide for the existing-resource path.
What is ADR?
ADR is a device identity and management layer that:
- Stores device metadata, attributes, and tags
- Manages credential policies for certificate issuance
- Decouples device identity from IoT Hub
- Enables multi-hub scenarios
- Provides query and update APIs
What is an ADR Namespace?
An ADR namespace establishes a management and security boundary for devices represented in ADR.
A namespace can include devices connecting to different IoT Hub instances, and is where you can enable new features like Microsoft-backed X.509 certificate management (preview).
Why ADR Matters
In traditional IoT Hub deployments:
- Device identity is tightly coupled to a specific IoT Hub
- Moving devices between hubs is complex
- Credential management is manual
- Metadata is limited
With ADR:
- ✅ Devices are represented and governed as Azure resources
- ✅ Namespaces provide a shared registry and security boundary
- ✅ Credential policies support certificate issuance
- ✅ Query and manage devices across hubs sharing a namespace
Certificate Management: Onboarding and Operational Credentials
Certificate management handles operational X.509 certificates used by a device to authenticate to IoT Hub after provisioning. It does not issue or manage the device’s onboarding credential. A device first authenticates to DPS with an onboarding method such as a symmetric key, TPM, or an existing X.509 certificate, then submits a CSR as part of the provisioning transaction. DPS validates the onboarding credential and uses the ADR CA and certificate policy referenced by the enrollment; the policy’s intermediate CA signs the operational certificate. The device private key remains on the device. Each ADR intermediate CA can have one certificate policy.
Certificate management is optional, but DPS is required for all IoT Hub preview scenarios, even when certificate management isn’t enabled. Operational certificates can be renewed and revoked, and ADR manages CA lifecycle and rotation operations. IoT Hub integration remains in public preview and isn’t recommended for production workloads.
Attestation Methods
Attestation is how devices prove their identity to DPS. Think of it like showing ID before boarding a flight. DPS supports three different "ID types":
1. Symmetric Key
- Simplest method
- Uses shared secret (enrollment group key)
- Device derives individual key:
HMACSHA256(groupKey, registrationId) - Good for development and testing
- Less secure than certificate-based methods
- 🆕 Can be combined with CSR – authenticate with symmetric key, receive X.509 certificate
2. TPM (Trusted Platform Module)
- Uses hardware security module
- Very secure
- Requires TPM chip on device
- Unique per device
- Not covered in this series
3. X.509 Certificate
- Industry standard for security
- Uses public key infrastructure (PKI)
- Supports certificate rotation
- Scalable with enrollment groups
- Two approaches:
- Traditional: Pre-provisioned certificates
- 🆕 CSR-based: Certificates issued during provisioning
- This is what we’ll focus on
High-Level Provisioning Flow with ADR
Here’s how the complete flow works with the new features:
The flow is shown in two stages to keep each diagram readable at article width.
Certificate issuance
sequenceDiagram
    participant Device
    participant DPS
    participant ADR
    participant CA as Issuing CA
    Device->>Device: Create keypair and CSR
    Device->>DPS: Attest and submit CSR
    DPS->>DPS: Validate enrollment
    DPS->>ADR: Request issuance by policy
    ADR->>CA: Select policy's issuing ICA
    CA-->>ADR: Issue certificate chain
    ADR-->>DPS: Return certificate chain
    DPS-->>Device: Return chain and Hub assignment
IoT Hub connection
sequenceDiagram
    participant Device
    participant ADR
    participant Hub as IoT Hub
    Device->>Device: Install chain and retain private key
    ADR->>Hub: Synchronize CA certificates
    Device->>Hub: Connect with operational X.509
    Hub-->>Device: Authenticate device
Alternative: Symmetric Key + X.509
This series defaults to X.509 bootstrap attestation followed by CSR-based X.509 operational certificate issuance. Symmetric-key onboarding is a supported alternative, not the default for this walkthrough.
One powerful pattern enabled by the new API:
- Phase 1 – Provisioning: Device authenticates to DPS using symmetric key (simple, pre-shared)
- Phase 2 – Operation: Device connects to IoT Hub using X.509 certificate (secure, Microsoft-issued)
Benefits:
- Easy initial provisioning (no pre-generated certificates)
- Secure operational communication (X.509)
- No need to distribute device certificates ahead of time
- Best of both worlds
When to Use DPS
✅ Use DPS when:
- Deploying many devices (10+)
- Devices need to be reassigned between hubs
- You want zero-touch provisioning
- Security is important (no hardcoded secrets)
- You need multi-tenancy support
- You want automated certificate management
- 🆕 You want Microsoft-managed certificate issuance
🤔 Consider if DPS is right for you if:
- Only a few devices (< 10)
- Devices never move between hubs
- Prototyping with connection strings is acceptable
Preview Feature Status
The IoT Hub integration with ADR and certificate management covered here remains in public preview. The current sample delegates DPS provisioning to the unified IoT SDK, so application code does not pin a DPS API version. For separate ADR registry-device ARM calls, the sample’s helper uses 2026-11-02-preview (Registry Devices REST API).
- ✅ CSR-based certificate issuance
- ✅ ADR credential policies
- ✅ DPS MQTT protocol support
- ✅ Microsoft-managed CA
The sorter uses the official unified SDK directly, with helpers for durable credentials. Don’t treat old wire-level examples as instructions to rebuild the removed transport.
Note: Check Microsoft’s current IoT Hub preview guidance before deployment.
For the current setup, see Microsoft’s ADR connected-services guide, CA hierarchy overview, managed CA setup, and certificate-policy and DPS-enrollment guide.
Next Steps
In the following sections, we’ll:
- Create DPS, IoT Hub, and ADR instances
- Configure credential policies for certificate issuance
- Set up enrollment groups (symmetric key and X.509)
- Build a .NET device application with the unified SDK and durable credentials
- Implement CSR generation and certificate management
- Integrate with ADR for device management